Deployment & migration

A flat network is one door into everything. Your data deserves better.

In a flat network, one compromised device gives access to everything. An intern, an external contractor, a former employee: if access is not compartmentalised, neither are the risks.

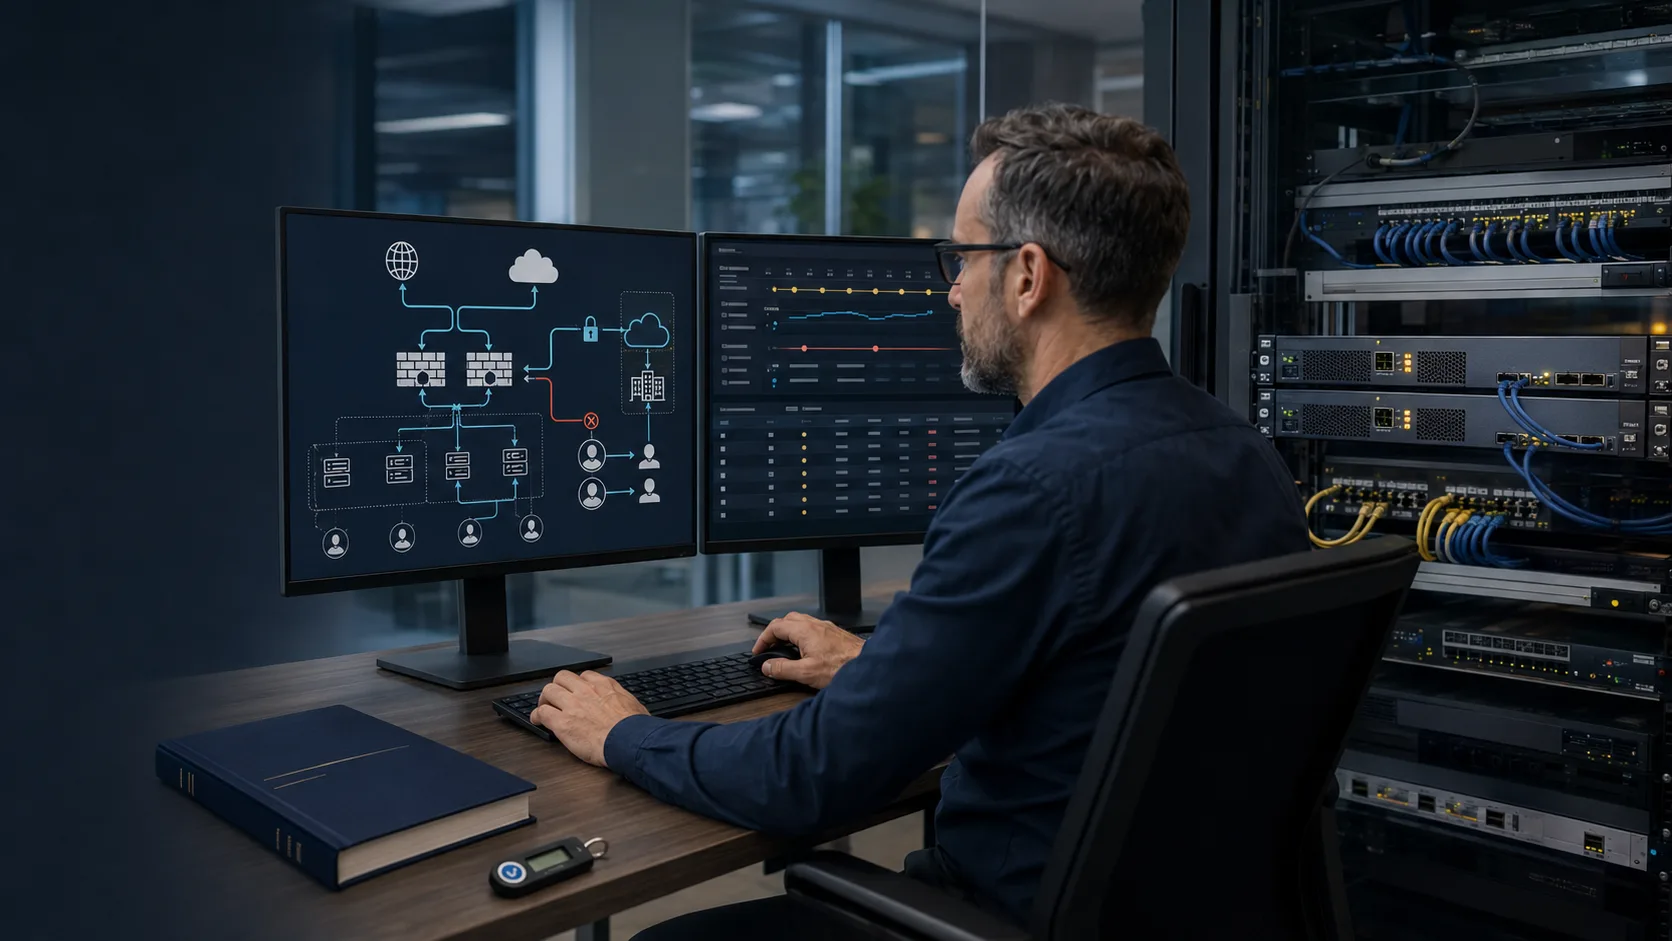
ARCrezo network security reduces your attack surface without blocking legitimate activity. Segmentation, access control, firewall rules — every layer is designed around your actual operations.

Book a call
Firewall and network access security

Does this sound familiar?

●Your network is not segmented and all devices communicate without restriction
●Vendors or third parties have access to your network and you cannot precisely control what they can reach
●You have compliance obligations (NIS2, key account clients) that require a defined level of network security
●You have experienced a security incident or want to prepare for one

Scope of work

✓Audit of existing access controls and segmentation
✓Design of the target security architecture
✓Implementation of network segmentation (VLANs, trust zones)
✓Firewall rule and filtering configuration
✓Remote access control (VPN, strong authentication)
✓Restriction of third-party and vendor access
What is not included
✕Application security (WAF, SIEM, EDR) — specialist partners can be engaged
✕Offensive penetration testing — ARCrezo network audits are defensive

Deliverables

✓Segmented and secured network infrastructure
✓Documented network security policy
✓Access matrix by profile
✓Configured firewall and filtering rules
✓Documentation of the secured architecture

How it works

01

Map

Identify data flows, access points and the zones to protect first.

02

Design

Define the target security architecture, segmentation and access rules.

03

Deploy

Implement segmentation, firewall rules and access controls.

04

Validate

Test rules, verify legitimate flows remain intact, document and brief teams.

Why ARCrezo?

✓Pragmatic approach: security that does not block legitimate usage
✓Heterogeneous environment experience: multi-vendor, multi-site, remote working
✓Complete documentation: your security posture is reproducible and auditable

Frequently asked questions

Will hardening affect our day-to-day usage?

Good hardening is transparent to legitimate usage. We always work with your teams to confirm that required flows are preserved.

Can we secure in phases?

Yes. We prioritise the most critical zones and progress in stages to minimise operational impact.

Does network security protect against ransomware?

It significantly reduces the attack surface and limits propagation, but overall security is multi-layered. We can refer you to specialist partners for complementary layers.

Is your network truly segmented? Check it with us.

Book a call